Website security. 中国信创-等保安全之网站安全反渗透
1
-
Version
Upload allow-list, XSS protection, login allow/deny lists and password policy
Bring compliance requirements into Odoo: restrict uploads, control file permissions, manage login sources and enforce password strength.
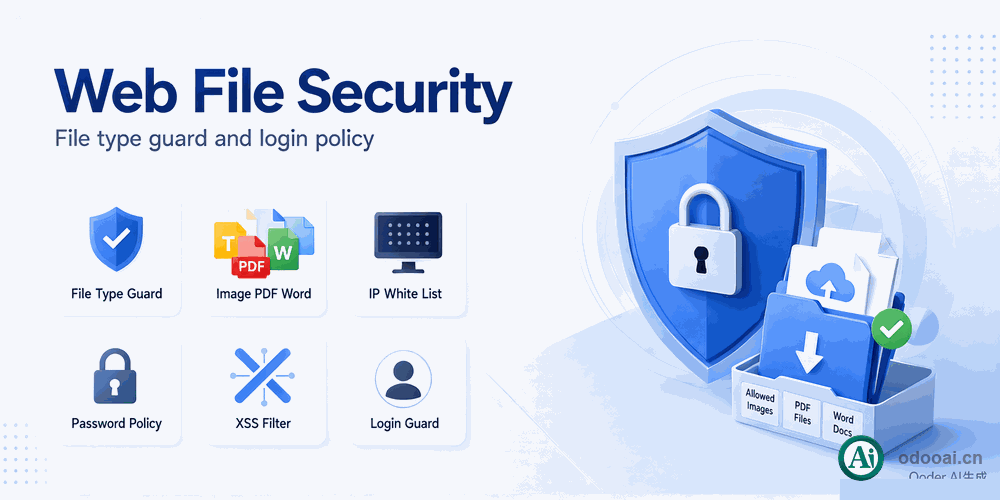
This module bundles hard controls for website and backend security: restrict uploads to images, PDF, Word and Excel; check Odoo file permissions at the OS level; limit XSS injection; configure remote login allow and deny lists; enforce password length, case, number and special character rules with expiry, retry limits and history. Suited to companies that must meet Chinese cybersecurity classified protection and CVE remediation requirements.
Upload allow-list, XSS protection, login allow/deny lists and password policy
Upload allow-list for images, PDF, Word, Excel and similar types
Check Odoo file permissions at the OS level
Restrict XSS injection and unsafe HTML
Configure remote login allow and deny lists
Enforce password length, case, number and special character rules
Password expiry, retry limits and history
Every capability included in this module
Full multi-language translation and global deployment. Native multi-company with strict data isolation.
Supports Odoo 20, 19, 18, 17, 16, 15, 14, 13, 12, Enterprise, Community and online SaaS.
Open source under LGPL-3, transparent and auditable, ready for customization.
Key screens of the module
Install Module
Configure Policies
Enable Password Rules
Verify Login and Upload
Professional Odoo Solutions: Implementation, Consulting and Training
| Version | 20.0, 19.0, 18.0, 17.0, 16.0, 13.0 |